10 Properties of Secure Open-Source Software

Case Studies
Whitepapers
Datasheets

Whitepaper

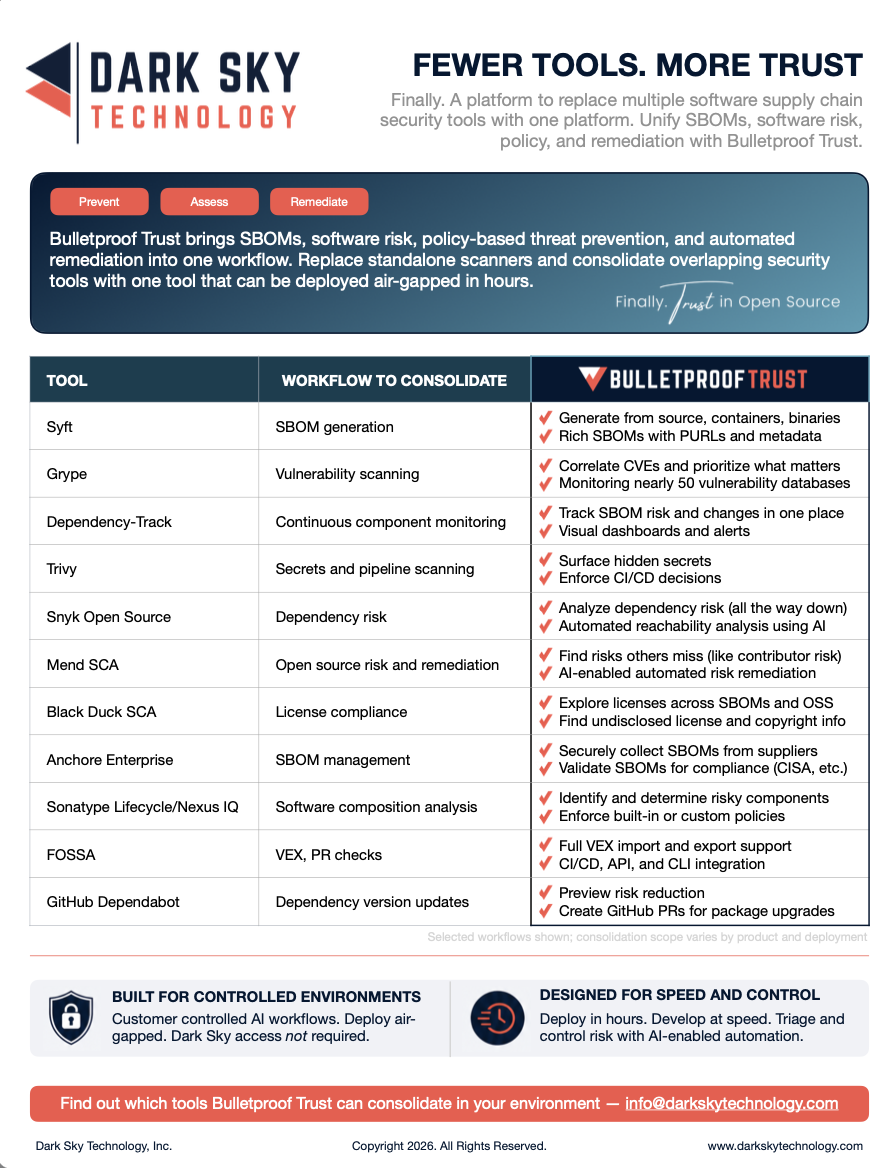
Fewer Tools. More Trust

Consolidating multiple disjointed tools into one workflow.

Finally. A platform to replace multiple software supply chain security tools with one platform. Unify SBOMs, software risk, policy, and remediation with Bulletproof Trust.

Whitepaper

Bulletproof Trust Firewall Case Study

The Vulnerability that Never Shipped

How Bulletproof Trust Firewall blocked a vulnerable dependency before release and helped close the remediation loop in under 15 minutes.

Do I really need to secure open-source software?

Whitepaper

In short, yes. Open-source software is written by unknown developers in untrusted companies running in foreign countries. Some of those developers are looking for any way to exploit your systems and software. Download our free whitepaper, 10 Properties of Secure Open-Source Software to (finally) secure the open-source and deploy your systems and software with confidence.

10 Properties of Secure Open-Source Software

Whitepaper

Pushwoosh Case Study

Foreign Influence and Deception in Open-Source Software

We get it. Nobody is doing this. Grab our free Whitepaper to learn how Bulletproof Trust detected a Russian company masquerading as an American company, destroying the trust of the Army and CDC.

Detecting Foreign Influence and Deception in our Open-Source Software

Whitepaper

Deploy Software with Open-Source with Confidence

We’re not salesy, but we get it. Grab our free Whitepaper, read up on our solution, and reach out when you’re ready…

Analyzing Open-Source Threats and Trustworthiness